



Self-hosted, data residency
Traffic and logs stay on your infrastructure, in the jurisdiction you choose. No mandatory cloud, no telemetry; the few outgoing connections (updates, definitions, certificates) are listed in the documentation.
ToutWAF, the self-hosted WAAP platform: WAF, API protection, anti-bot, layer-7 anti-DDoS and client-side security, driven from a single console. It also looks after what surrounds your sites: servers (live dashboards, security audit, one-click fixes), endpoint antivirus and a mail gateway. Detection mode first, blocking when you are ready.
Dozens of Linux distributions and versions, Windows, Docker and Kubernetes, on x86_64 and 64-bit ARM.
Linux Mint / LMDE, Pop!_OS, Zorin OS, elementary OS
Stop stitching together a WAF, an API gateway, a bot tool and a DDoS shield. ToutWAF unifies them.
OWASP Top 10, CRS and SecLang, virtual patching.
Route profile, JWT, GraphQL limits, discovery; schema validation under licence.
Fingerprinting, challenges, bot score, AI crawlers.
Multi-key rate limits, flood detection, HTTP/2 abuse.
CSP generator, third-party script inventory, skimmer patterns.
Every request goes through one pipeline: lists, geo, reputation, limits, anti-bot and signature detection with anomaly scoring.
$ curl -i "https://shop.example.com/?id=1' OR '1'='1"
HTTP/2 403
x-toutwaf: blocked
x-toutwaf-code: TW-2001
rule: sqli.tautology  score 15/5
From signature detection to server, endpoint and mail security: every function says whether it is free or needs a licence. No cloud lock-in.
Injections, deserialization, request smuggling, uploads, scanners and CMS attacks, inspected on every request in detection or blocking mode.
A route profile in learning mode first, OWASP API Top 10 coverage, tokens, keys and GraphQL limits; schema validation and consumer plans under licence.
An explainable bot score, challenges, verified crawlers, TLS fingerprints, an AI crawler policy and abuse limits.
Limits per key, flood detection, an under-attack mode and connection guards against slow attacks and HTTP/2 abuse.
Lists, countries, reputation and automatic bans; country degrees, thresholds and simulation under licence.
ToutWAF settles its own false positives and moves a site from observation to blocking, with evidence you can audit and undo.
Run ToutWAF for several clients from one console: one organisation per client, quotas, isolation, invitations and reports per client. The default organisation is free, the rest is under licence.
Add your existing servers and watch over them from the same console, with a small agent for Linux and Windows that only opens outbound connections.
Back up the console and the servers you supervise, with restore tests; a standby console takes over when you decide.
A Postfix and Rspamd gateway that ToutWAF installs and manages over SSH on a server of yours, in front of your real mail server. No free tier.
A customisable console in 10 languages, including right-to-left Arabic, reached under a secret path.
The installer checks your system first. One command on a supported Linux, a script on Windows, or the Docker and Kubernetes files.
Enter the domain and the origin. ToutWAF gets the certificate, detects your stack and proposes a policy template.
Detection mode runs first. Review the report, switch to blocking in one click, and roll back in one click too.
A WAF that blocks the wrong requests costs more than it protects. ToutWAF starts in detection mode, shows what it would have blocked, lets you test a change on past traffic and explains every decision. It cannot promise zero false positives, and no figure is published for it.
Detection mode is the default. At the end of the observation period a report proposes narrow exceptions for the recurring false positives.
Replay recorded traffic against a draft policy and see what it would have blocked.
Switch to blocking in one click, or roll it out on a share of nodes or requests first, and roll back in one step.
TW-2001Impact preview: 0.01% of the last 7 days of traffic would be affected.
Built for organisations that must keep control of their data.
Traffic and logs stay on your infrastructure, in the jurisdiction you choose. No mandatory cloud, no telemetry; the few outgoing connections (updates, definitions, certificates) are listed in the documentation.
IP pseudonymisation, log minimisation, masked payload capture, configurable retention, and export or erasure by address.
A verifiable audit trail and evidence mapped to controls (PCI DSS 4.0, NIS2, DORA, ISO 27001, SOC 2) from the live state of the platform. It is evidence, not an attestation: ToutWAF holds no certification.
Real screenshots of the console: live dashboards, security score A to F, one-click fixes and a look you can make your own.
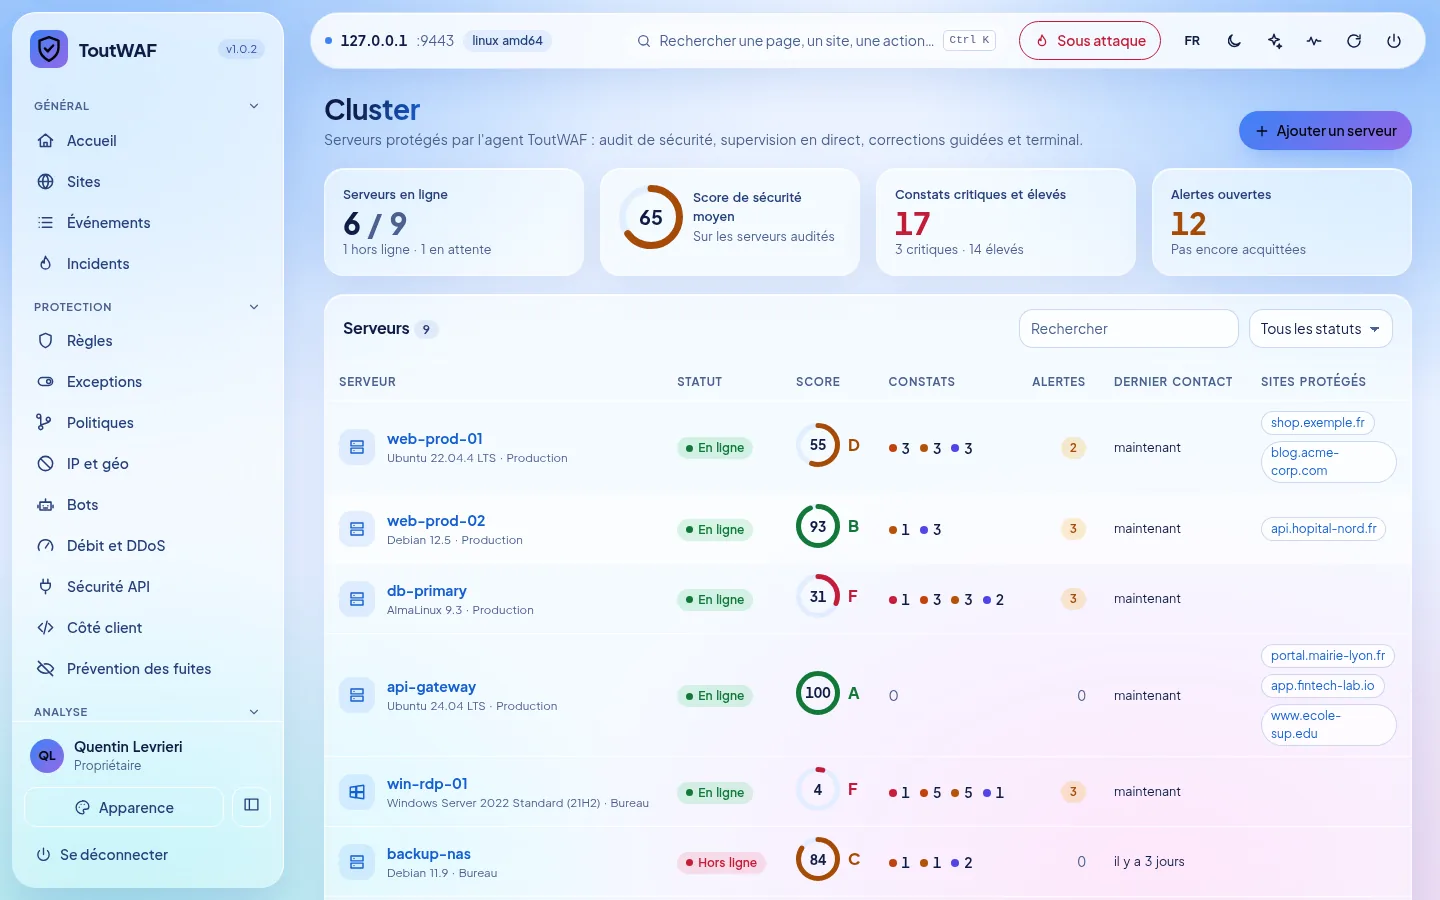
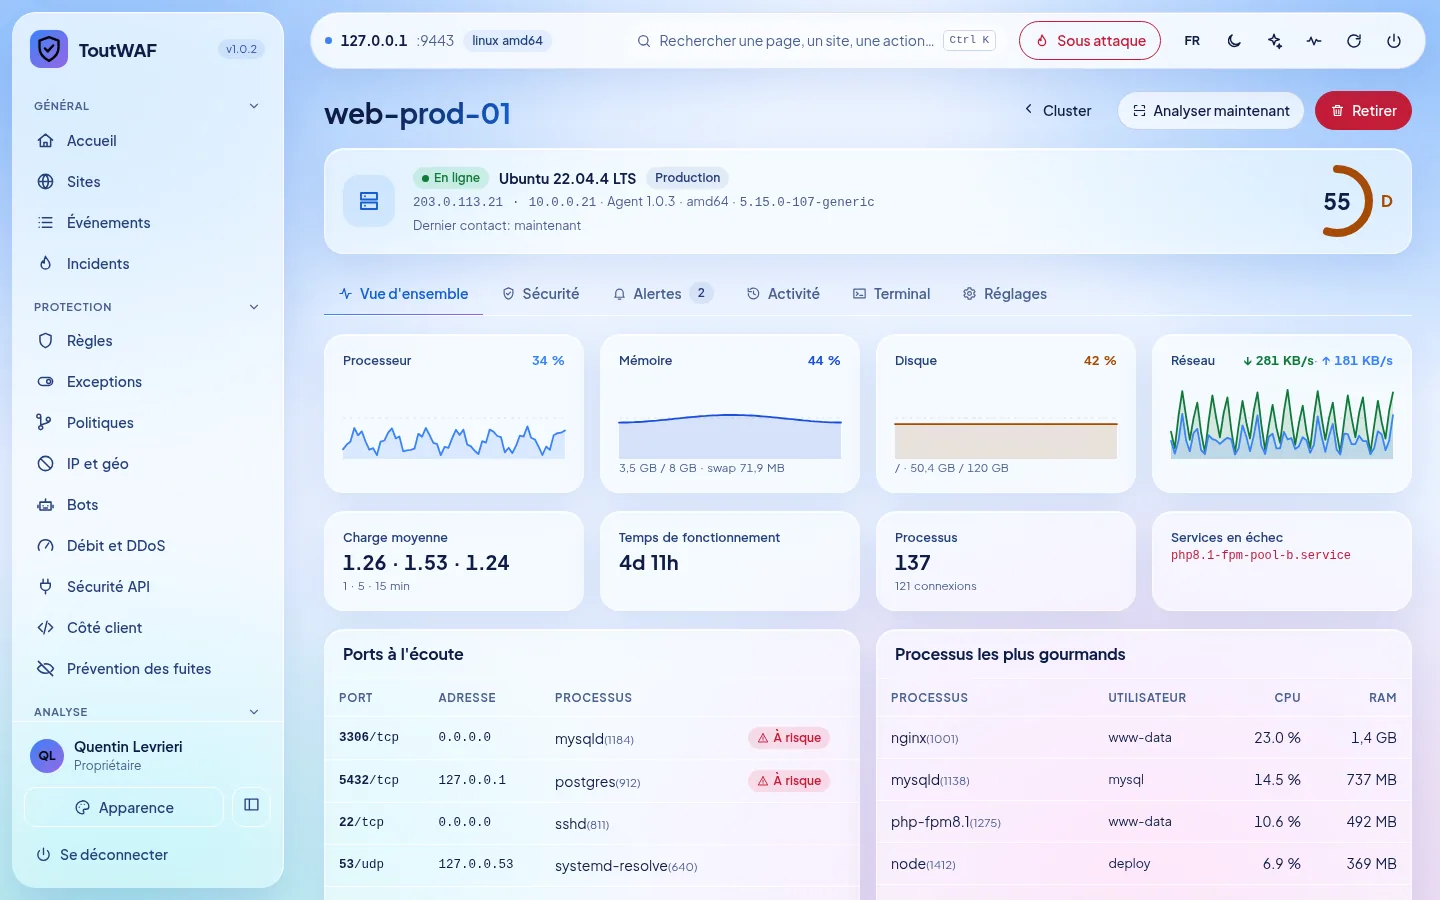
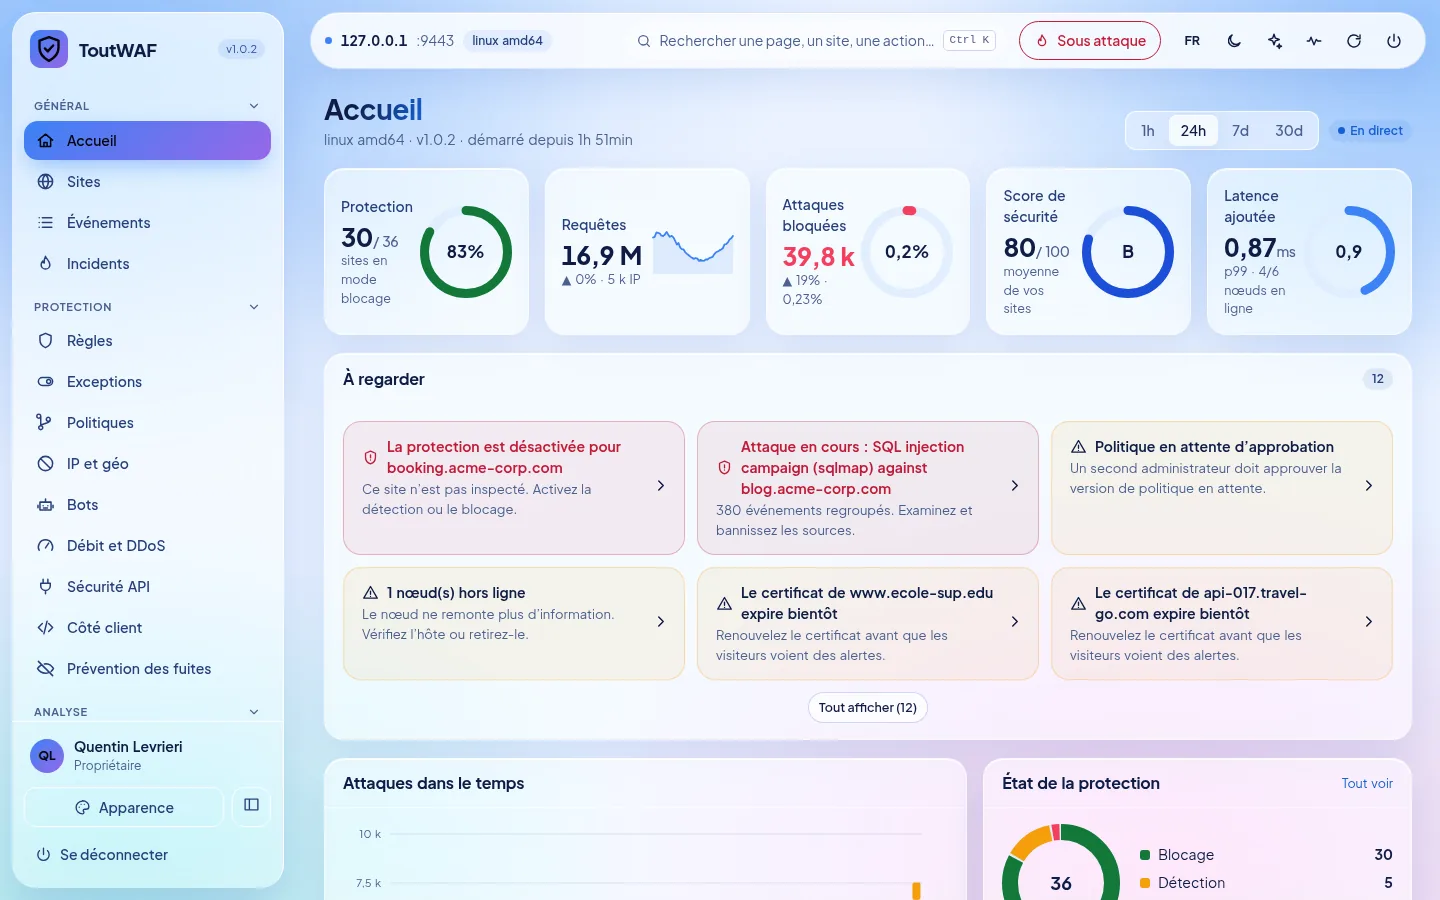
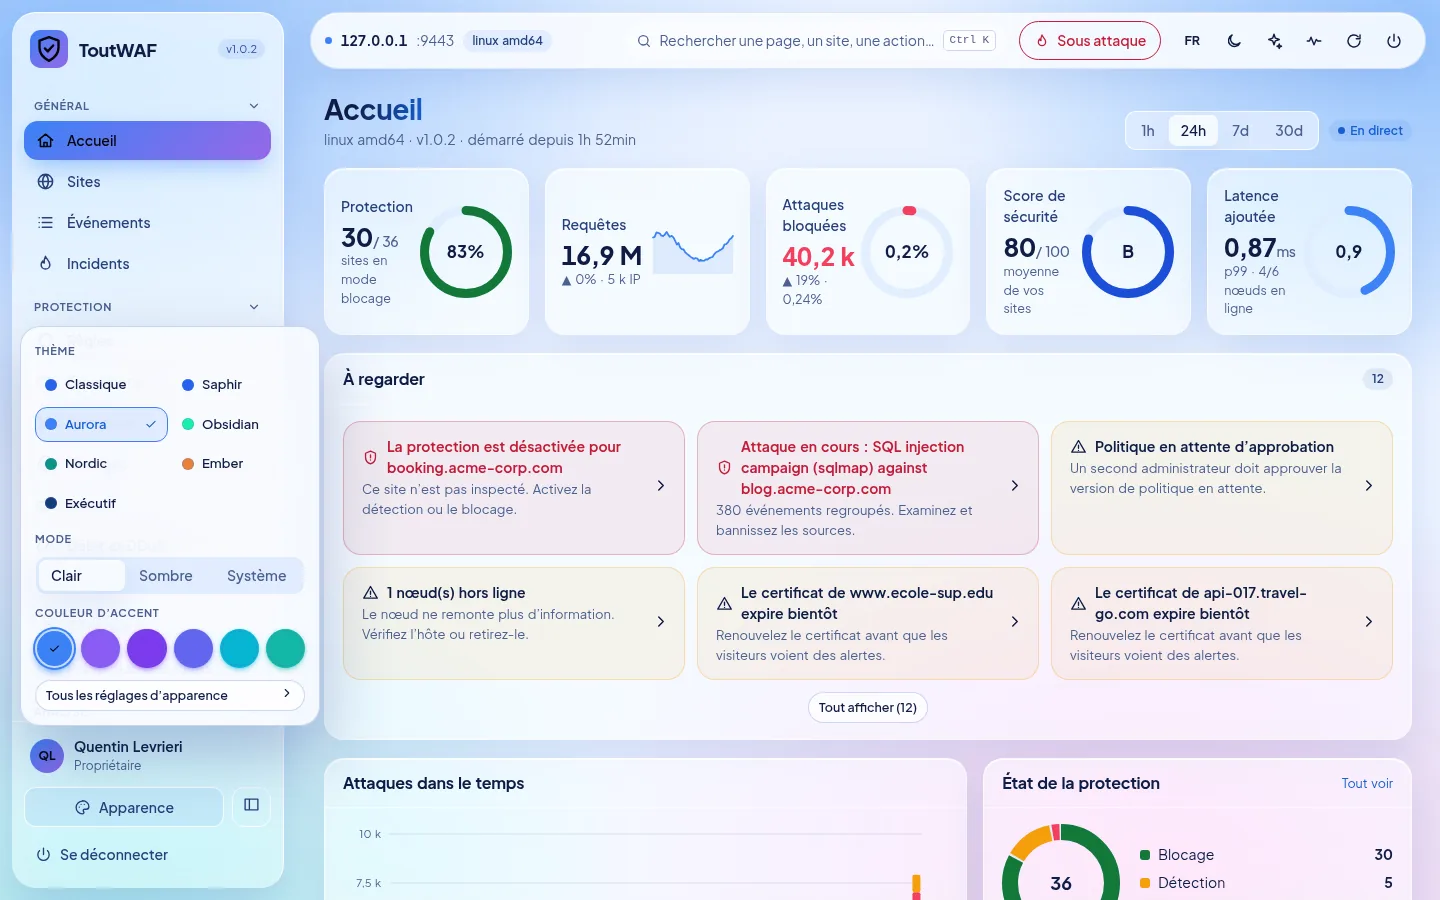
The ToutWAF console gives you full control: live attacks, explained events, sites, rules, bans and certificates, with seven themes, light and dark modes and a layout that works on a phone. Illustration with demonstration data.
Install it on your own server, or get in touch to talk about licences.