ToutWAF is a complete WAAP with a suite of tools around it. Every function listed here exists in the product today, with its edition: free, or licence required. Some of them have not yet been tried in real conditions and carry a tag that says so. What is not built, withdrawn or not verified on real systems is listed at the bottom of this page.
EditionFree Included in every offer, including both free offers (Free and Free +)Pro and above Paid offers: visible in the console, locked without a licence. From Pro, unless Agency or Enterprise is shown
Not yet tried in real conditions Works in the product's tests, but has not yet been tried with the real service, system or equipment. The console shows the same note where you set the function up.
A function under licence stays visible in the console, locked and never hidden. Where a function has a free basis and an advanced part under licence, both are listed. When a paid licence ends: 48 hours of grace, 48 hours of read-only, then WAF protection is switched off (traffic keeps flowing, unprotected) until renewal.
Functions in detail
Dedicated pages: how it works, illustrations, use cases, and what is free or under licence.
Site self-test: ordinary requests evaluated through your data plane before anything is blockedFree
Estimated false-positive rate per rule group and the Ready to block indicatorFree
CRS plug-ins for the technology detected on your siteFree
Journal of automatic decisions with the evidence, and one-click undoFree
Automatic profile: log only, then challenge, then block, one rule group at a timePro and above
Automatic exceptions: narrow, expiring, created only from strong evidence in real trafficPro and above
Automatic rollback of a rule update that blocks ordinary requestsPro and above
Definitions and threat intelligence
About 85 sources of rules, reputation lists and tables, kept up to date by the control plane. Nothing about your visitors is sent.
About 85 sources checked every hour, verified before use and rolled back if they failFree
Essential package on by default: web rules, known exploited vulnerabilities, Tor, large free address lists, CDN networksFree
Pro and Maximum packages: broader address lists, phishing domains, AS table, City tablePro and above
Explainable IP reputation score from 0 to 100: list class, agreement of independent providers, freshnessFree
Offline mode with signed bundles for servers without Internet accessFree
Look-up of an indicator or an address from the consoleFree
Licence or terms of every source shown; lists with restricted terms stay off until you accept themFree
Precision of each list measured on your own trafficPro and above
Adjustable points for each reputation classPro and above
Weekly watcher of public registries that proposes new sources and flags dead onesPro and above
Your own keys for lists that need one, stored encryptedPro and above
Known exploited vulnerabilities (CISA KEV) tracked every 6 hours and tied to virtual patches when a verified pattern existsFree
Technology detection that proposes the right template and CRS plug-insFree
API security
A route profile in learning mode first, OWASP API Top 10 coverage, tokens, keys and GraphQL limits; schema validation and consumer plans under licence.
Invisible proof-of-work, JavaScript check or built-in privacy-friendly CAPTCHAFree
Cloudflare Turnstile, hCaptcha or reCAPTCHA as an explicit option (the visitor's address then goes to the provider) Not yet tried in real conditionsFree
Crawlers verified by reverse DNS: a fake Googlebot is blockedFree
AI crawler policy (GPTBot, ClaudeBot and others): allow, log, challenge or blockFree
JA3 and JA4 TLS fingerprints, usable to deny tools and to limit ratesFree
AI assistant: explains an event, an incident or a site and suggests a rule that stays disabled until you save itFree
Works offline with built-in answers; an external provider is your explicit choiceFree
Questions built from summaries, never from visitor records; a request excerpt only when you press the buttonFree
Private language model on your own server (Ollama or OpenAI-compatible): no question leaves your network Not yet tried in real conditionsEnterprise
Traffic delivery and load balancing
Several servers behind one site: weights, route pools, health checks and safe retries; advanced algorithms, session persistence and canary rollouts under licence.
Weighted round robin, backup servers, passive health checks, safe retries and a circuit breakerFree
Route pools: send a path, host, header, method, country or A/B share to its own group of serversFree
Timeouts, keep-alive and HTTP/1.1, HTTP/2 or h2c towards the origin; TLS to the origin with your own CAFree
In-memory cache for static responses, with purgeFree
Brotli, zstd and gzip compressionFree
Rewrites, redirects and custom error pagesFree
Block page in 10 languages with an incident ID; your site name, colour and logo appear next to the fixed ToutWAF mentionFree
Real client address from the PROXY protocol, trusted X-Forwarded-For or CF-Connecting-IPFree
Several protection nodes: proposed DNS records for the nodes in service and a check of what your DNS answers; keepalived files for a virtual address; ToutWAF manages no DNS Not yet tried in real conditionsFree
Other algorithms: least connections, IP hash, consistent hash, random, two choices, fastestPro and above
Session persistence by cookie, address or headerPro and above
Active health checks and fine tuning of the circuit breakerPro and above
Maintenance of a server or a node without cutting a single request (drain)Pro and above
Canary and blue/green rollouts by share of requests, and slow startPro and above
Events and observability
Structured logs, an explained event view, search, incidents, metrics and traces, kept on your installation.
Executive or technical PDF reports, on demand or scheduled (weekly or monthly), sent by e-mail or through an integrationFree
Evidence for PCI DSS 4.0, NIS2, DORA, ISO 27001 and SOC 2, computed from the real state; it is not an attestationFree
Privacy: address pseudonymisation, retention of events and addresses, log minimisation, masked fieldsFree
Right of access and erasure for an IP address: export, then erasure of events, incidents and bansFree
Security score per site, with the list of improvements to makeFree
ToutWAF Doctor and go-live
One check from the machine to the origin of your sites, with the cause and the action to take, your own values already filled in.
One diagnostic from the machine up to the origin: node, policy, ports, firewall, DNS, certificate, Internet access, originFree
Each finding comes with its cause and the action to take, in plain wordsFree
DNS check for IPv4 and IPv6 that recognises a CDN or proxy address left over in an AAAA recordFree
Go-live assistant: node, DNS, ports and certificate in four rows, certificate ordered only when everything is greenFree
Optional test from the Internet, through the staging server of a certificate authorityFree
Help for your router, box, cloud security group or firewall, with your values filled in (files for OPNsense and pfSense) Not yet tried in real conditionsFree
Text report to send to support: nothing about your visitors or the content of your pagesFree
Servers and host agents
Add your existing servers and watch over them from the same console, with a small agent for Linux and Windows that only opens outbound connections.
Add a server with a generated install script or an installation over SSHFree
Small agent for Linux and Windows that only opens outbound connectionsFree
Live dashboard per server: CPU, memory, disks, network, ports, processesFree
Security score from A to F, with an audit of access, network, updates, system, web server and malwareFree
19 guided one-click remediations with preview, undo and lock-out guardsFree
Intrusion alerts on 13 kinds of change: new ports, accounts and SSH keys, brute force, changed files, web shellsFree
Antivirus scans with ClamAV on Linux and Microsoft Defender on Windows, with quarantineFree
Remote terminal in the browser: reserved to its owner, audited, no SSH port to openFree
SSH install pinned to the host-key fingerprint you confirm first; credentials are used once and never storedFree
One ToutWAF protection node, installed over SSH or with a generated command, with its country flag, version and synchronisation stateFree
More than one protection node, installed and kept in step from the consolePro and above
Remote installation of ToutPanel, the web hosting panel, on a fresh server, then of its web stack (Nginx, MariaDB, PHP 8.5 by default) Not yet tried in real conditionsFree
ToutPanel web servers: link by command or over SSH, with a dedicated token, a pinned certificate and a heartbeat; ToutWAF becomes the panel's WAF engine once ToutPanel delivers its part Not yet tried in real conditionsFree
ToutPanel integration and websites
Create a site in ToutPanel and ToutWAF in one operation, add aliases, and keep the two products reachable from each other.
Creating a site from the console: ToutPanel site, database, FTP account, DNS zone, certificate and backups as chosen, then the protected site, with undo if a step failsFree
Host-name aliases after creation: the ToutPanel site, the protected site, the policy and the certificate are updated togetherFree
firewalld « keep-open » guard: restores ToutWAF's access to the web server's ports if a rule cut it (never tried against a real firewalld in production)Free
« Behind ToutWAF » check of a panel site, in five verifications (not yet tried against a real ToutPanel)Free
Server monitoring
The health of the servers behind your sites: resources, services, certificates, updates and backups, with thresholds, alerts and a history kept on your installation. The first server is free.
First supervised server free: processor, memory, swap, disk, inodes, load, network, services, ports and processesFree
Local certificate expiry, pending security updates, age of the last backup, silence of the agentFree
25 default alert rules by kind of server (web, database, mail, DNS, containers), with attention and critical thresholdsFree
Alerts per server, measure and element, acknowledgement and a back-to-normal noticeFree
Rules and thresholds of your own, for the measures you choosePro and above
More than one supervised serverPro and above
History kept on your installation: 30 days of detail and 365 days of hourly averages, adjustableFree
Availability probes from your installation: HTTP, TCP and TLS certificate checks (3 free)Free
More than 3 availability probesPro and above
Tells the WAF when a server that hosts an origin runs out of resourcesFree
Supervision-only mode: the agent never runs a fix, a scan, a restore or a terminal on that serverFree
Host security: inventory of packages, accounts, SSH keys and scheduled tasks, with a vulnerability lookup done on your console (your package list never leaves it)Pro and above
Integrity of the files you choose and 25 read-only hardening checksPro and above
Backups and standby console
Back up the console and the servers you supervise, with restore tests; a standby console takes over when you decide.
Scheduled local backup of the console, with a restore test after every backupFree
Guided restore with a preview, an automatic restart and rollbackFree
No secret in clear in a backup: keys, tokens and passwords are sealed with the master keyFree
Backup plans of the linked ToutPanel, started from the same pageFree
Off-site targets: S3, SFTP, WebDAV or a commandPro and above
Backup server: files and databases (MySQL, MariaDB, PostgreSQL) of supervised servers, encrypted with a recovery key only you keep, verified by a restore testPro and above
Standby console: an encrypted, verified copy every hour and a guided, manual takeover Not yet tried in real conditionsAgency and above
Taking over from a standby console is never locked, even without a licenceFree
Mail security gateway
A Postfix and Rspamd gateway that ToutWAF installs and manages over SSH on a server of yours, in front of your real mail server. No free tier.
Inbound gateway in front of your mail server, installed and managed over SSH on a dedicated Linux server Not yet tried in real conditionsPro and above
Anti-spam and anti-phishing, attachment policy, optional antivirus, quarantine Not yet tried in real conditionsPro and above
Data-loss prevention on messages Not yet tried in real conditionsPro and above
Sender verification (SPF, DKIM, DMARC), greylisting, impersonation and link detection: all off by default Not yet tried in real conditionsPro and above
Never an open relay: every configuration is checked; if the filter stops, mail is held, not lost Not yet tried in real conditionsPro and above
Optional outgoing mail: relay, DKIM signing, sending limits Not yet tried in real conditionsPro and above
Mail doctor, daily digest of the quarantine, reports and exports Not yet tried in real conditionsPro and above
Nothing about your mail goes to a third party by default; message content is never in the audit log Not yet tried in real conditionsPro and above
Tenants and MSPs
Run ToutWAF for several clients from one console: one organisation per client, quotas, isolation, invitations and reports per client. The default organisation is free, the rest is under licence.
Fleet page: nodes, versions, enrolment tokens and orchestrated updates of the nodesFree
Licence: a signed key checked on your machine, with no check over the network; at expiry, 48 hours of grace then 48 hours of read-onlyFree
Integrations
Six notification types are free; 45 modules in all for SIEM, chat, ticketing, SOAR and threat intelligence, under licence. Your existing proxies and CDNs work with ToutWAF.
Alert notifications: e-mail, generic signed webhook, Slack, Microsoft Teams, PagerDuty, OpsgenieFree
SIEM and logs: Syslog (CEF, LEEF, JSON), Splunk, Elastic and OpenSearch, Microsoft Sentinel, QRadar, ArcSight, Wazuh, Graylog, Datadog, Loki, OpenTelemetry Not yet tried in real conditionsPro and above
More chat and paging: Discord, Google Chat, Mattermost, Telegram, ntfy, Pushover, Rocket.Chat, Webex, Zulip, GotifyPro and above
Ticketing: Jira, GLPI, ServiceNow, GitHub and GitLab Issues, Linear, Redmine, Zendesk Not yet tried in real conditionsPro and above
SOAR and automation: n8n, Shuffle, Zapier, TheHivePro and above
Threat intelligence: MISP in both directions, STIX/TAXII (OpenCTI and others), CrowdSecPro and above
Existing reverse proxies ask ToutWAF for a decision: nginx, Caddy, HAProxy, Envoy, TraefikFree
Behind or in front of a CDN or cloud load balancer, with the real client address (PROXY protocol or trusted headers)Free
Policy files for Git and CI, an Ansible role, a Helm chart and an API client for TerraformFree
Git link (off by default, experimental): the configuration lives in a Git repository, ToutWAF computes a plan and applies it after checks Not yet tried in real conditionsPro and above
Firewall and VPN (optional modules)
Two modules that are off by default and not yet proven in production: try them first on a machine you can reach another way.
Firewall: inbound, outbound and forwarded rules loaded with nftables, aliases, NAT, OPNsense and pfSense import, history (not yet proven in production)Free
Guard against locking out the console and SSH, and automatic return of the rules after 60 seconds without confirmation (not yet proven in production)Free
VPN: WireGuard, OpenVPN and IPsec/IKEv2 servers with their clients; the configuration is generated and kept, no tunnel is started (not yet proven in production)Free
Outgoing connections from this machine to an existing VPN (WireGuard, OpenVPN), without replacing the default route unless explicitly asked (not yet proven in production)Free
One switch per module in Settings > Modules, reserved to platform administrators; switching a module off hides it and deletes nothingFree
Scheduled tasks
Safe maintenance actions at fixed times: backup, journal export, certificates, lists, Doctor and e-mail report.
Six built-in actions: configuration backup, journal export and rotation, certificate check, list update, Doctor, e-mail reportFree
Five-field schedules or simple repetitions, time zone, single run, preview of the next runs and catch-up of a missed runFree
One run at a time per task, time limit, bounded history with truncated output and masked secrets, alert after two failures in a rowFree
Actions on a linked ToutPanel web server (service, cache, backup): reserved to platform administrators and off by defaultFree
Installation and deployment
A one-line installer for Linux and Windows that checks your system first, an all-in-one install, Apache or Nginx as the origin, Docker and Kubernetes files, and an updater in the console.
One-line installer for Linux and Windows, as a menu or unattended, in 10 languages, with a SHA-256 check and a signature check when a release key is setFree
Compatibility check before any change: systems tested, expected or unsupported, from the installer's own dataFree
Environment check: busy ports, web servers that restart at boot, closed firewall, with the cause and the actionFree
All-in-one install: the local data plane enrols itself, nothing to type afterwardsFree
Apache or Nginx as the origin: the Origin server card examines it and writes the files for the real visitor address and HTTPS; ToutWAF never changes your serverFree
Published matrix of installation modes: tested, partial, not tested or unsupportedFree
All-in-one image for Docker Compose (tested on Linux amd64) and a Helm chart, supplied with your distributionFree
Standalone data plane driven by a YAML file with hot reload; offline installation from a local archiveFree
Updates from the console: choice of channel (dev for now, as no stable version exists yet), release notes, Update now with progress and automatic rollbackFree
Host firewall opened by the installer when firewalld or ufw is active; a card in Settings to check and open portsFree
First-run wizard with technology detection that shows the layers found, a confidence level and the evidenceFree
Console and languages
A customisable console in 10 languages, including right-to-left Arabic, reached under a secret path.
Seven themes: Classic, Sapphire, Aurora (default), Obsidian, Nordic, Ember, Executive; light and dark modes, accent colourFree
Console and installers in 10 languages, including right-to-left ArabicFree
Console served only under a secret path, with a one-time setup linkFree
Help next to each setting, a loading animation, a layout that works on a phone, a collapsible menuFree
Floating task window that follows installs, updates and certificate ordersFree
The console, as it really looks
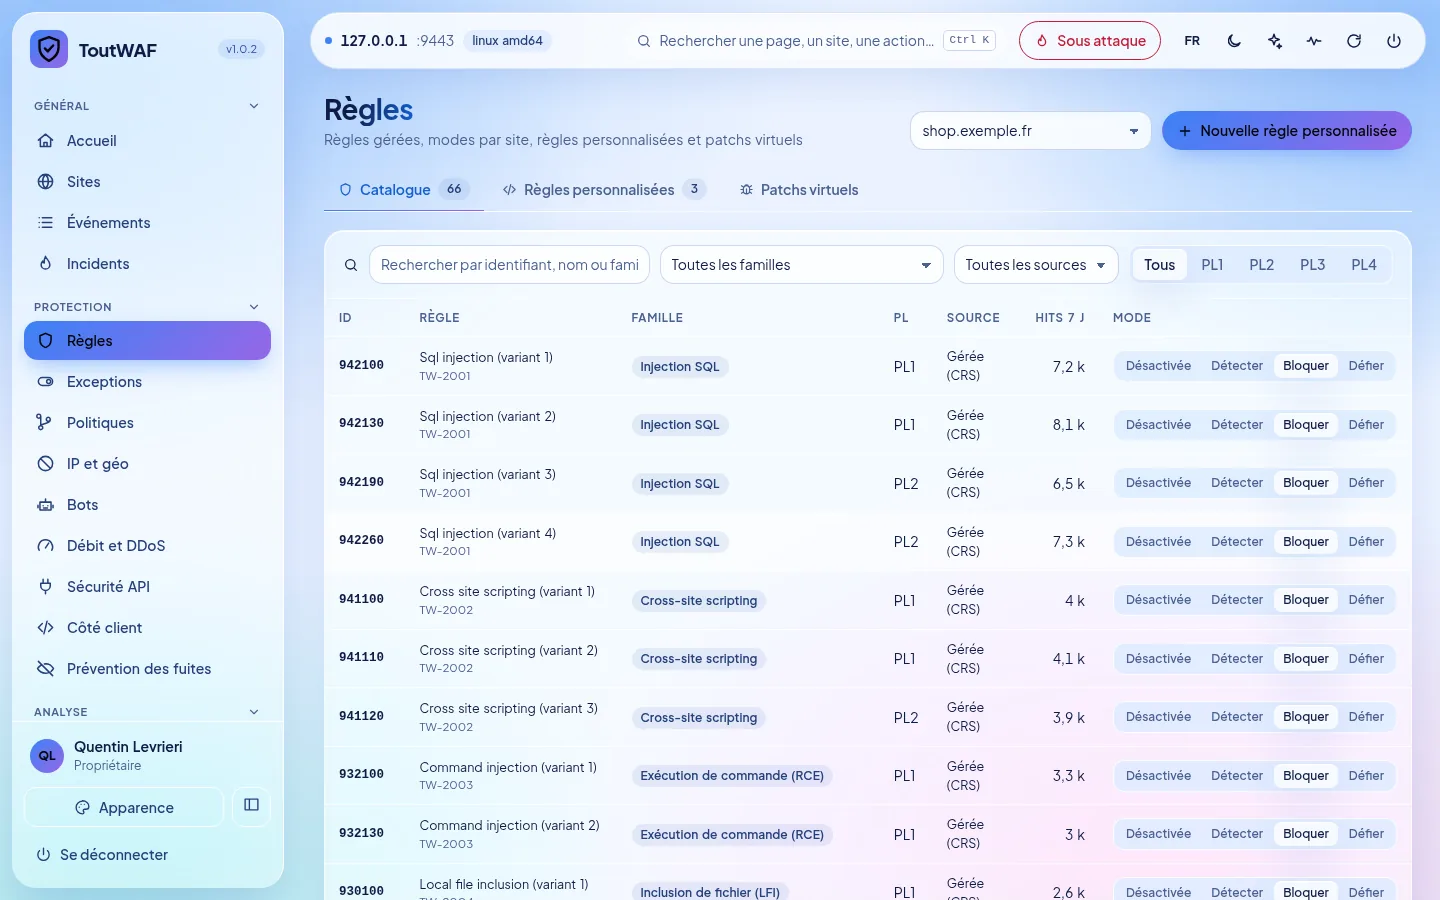
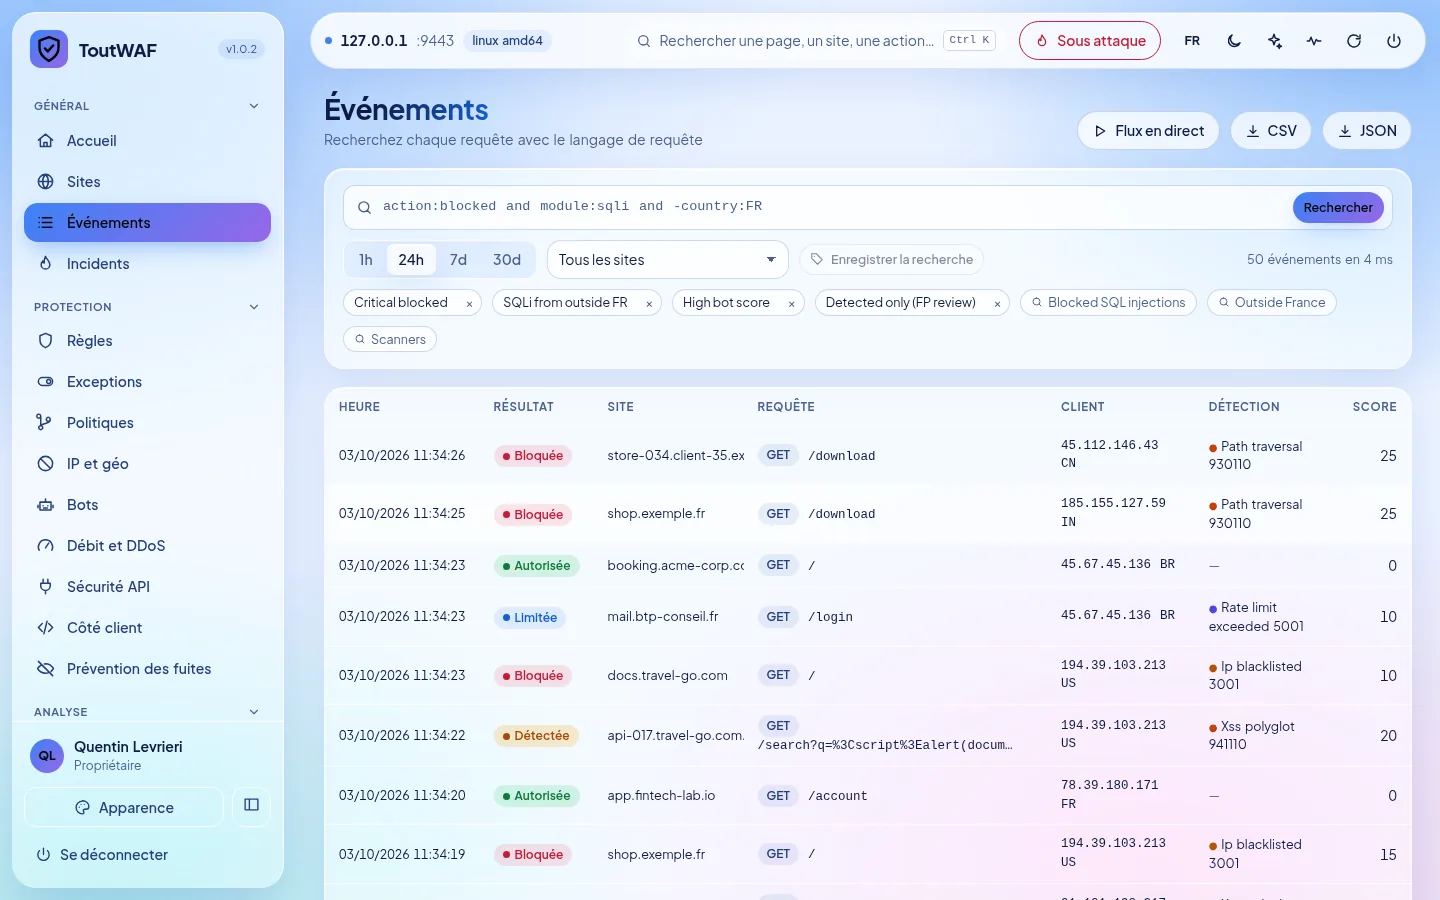
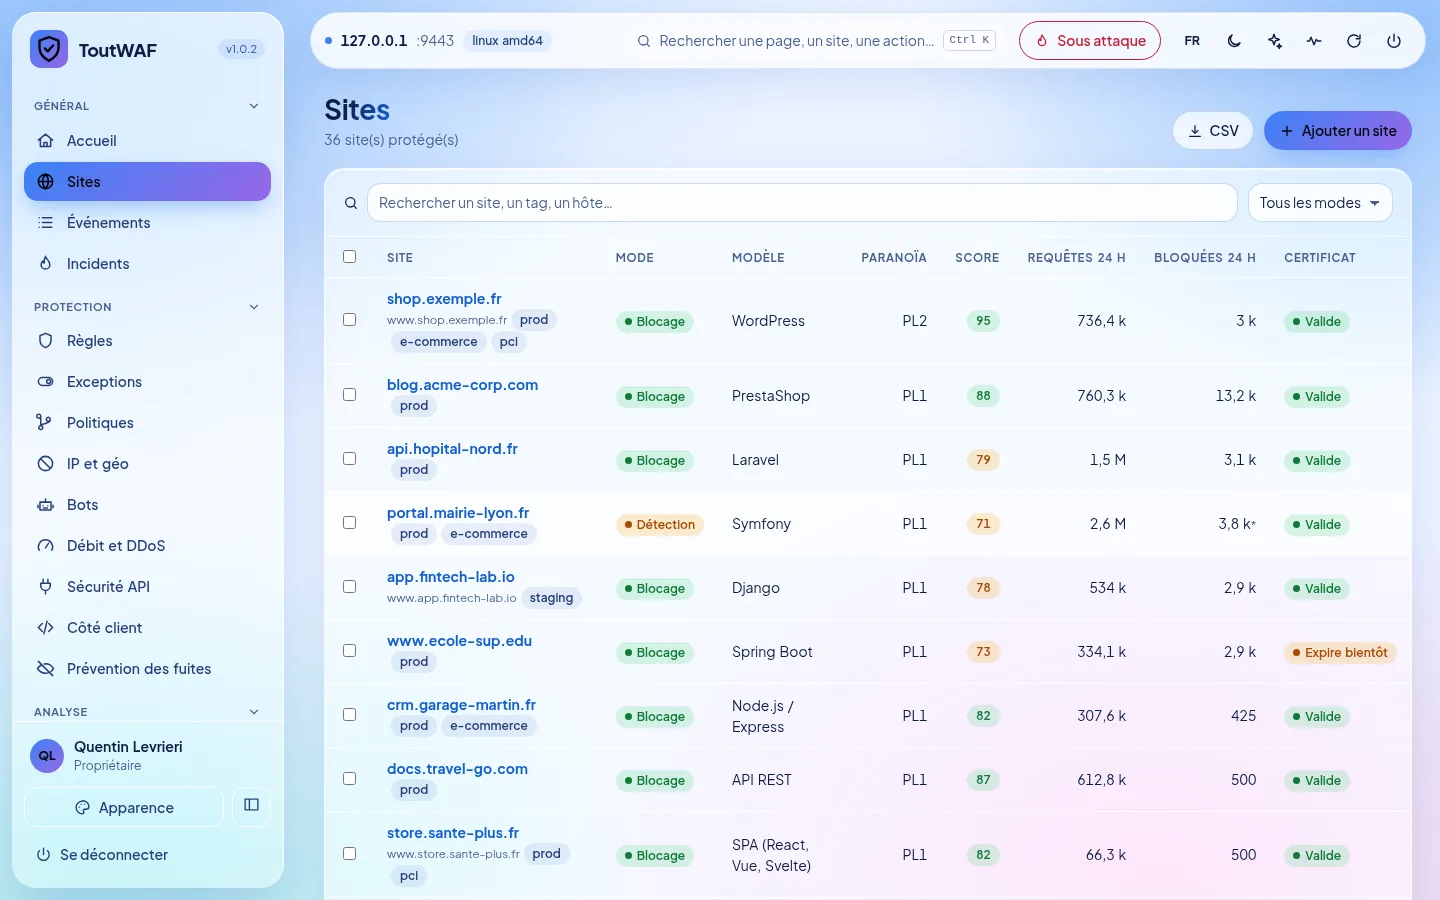
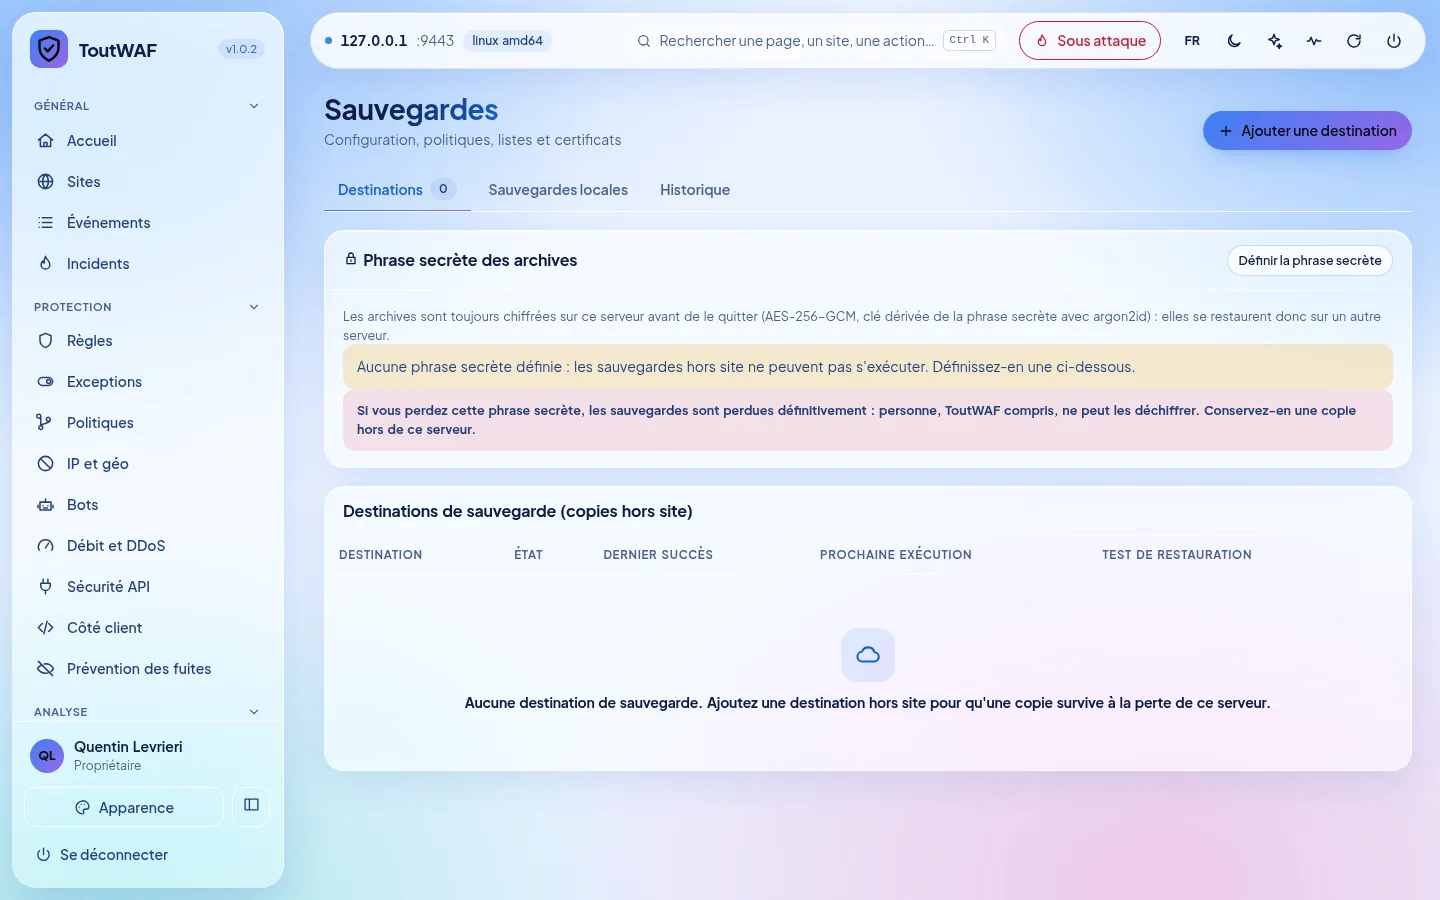
Screenshots taken from the product: rules, events, sites and backups.
Rules: enable, tune and test detection rulesEvents: every request decision, explainedSites: protected domains, certificates and modesBackups of the configuration
What is not in this release
ToutWAF says what it does not do yet, or has not been able to verify, so that you do not find out in production. The details and the full list of known limits are in the documentation.
Not built
Not built yet
HTTP/3: the option is ignored and UDP port 443 stays closed
A clustered control plane: one active console, plus a standby console that you promote by hand
PostgreSQL: the console uses SQLite (ClickHouse is optional for events)
Detection of content scraping and stock hoarding, and leaked-password checks
Partial
Preview or partial
Collective defence network: withdrawn from this version (no menu, no page, no licence line). It was only a local preview, and nothing was ever sent anywhere
Terraform: an API client only, without provider resources; the Kubernetes operator is CRDs and a skeleton
Antivirus: a first version exists (EICAR, SHA-256 signatures from free lists, no anti-ransomware) but it is offered in no plan for now; it does not replace a complete antivirus
Rate-limit counters, bans and baselines are kept per node, not shared between nodes
Envoy and HAProxy call an HTTP decision endpoint: no gRPC ext_authz and no SPOE agent
Unverified
Not verified on real systems
A clean installation on every listed system, and the antivirus agent on Windows, macOS and arm64: no real Windows, macOS or arm64 hardware was used, only containers and emulation
A real ToutPanel: the link and the web stack installation were tried against stand-ins
Routers and firewalls, kernel blocking and a virtual address: the files for OPNsense and pfSense were never tried on a real router, the kernel helper never ran under a real systemd, and no real keepalived failover was tested
Real certificate authorities, SAML sign-in, SIEM and ticketing services, external CAPTCHA providers and a private language model server: tried against stand-ins
Mail gateway: the Postfix daemon never ran and no real mail was received or delivered. Standby console: tried between two local consoles only
By design
Not done, by design
ToutWAF never manages your DNS: it tells you what to create and checks it
ToutWAF handles no payment and no invoice: you bill your clients from the usage export
No white label: the ToutWAF brand stays on every page and report; a client's name and logo are added next to it
No certification is claimed (PCI DSS, ISO 27001, SOC 2, ANSSI CSPN): ToutWAF provides evidence, not attestations
The 10 languages were written with the help of AI and have not been reviewed by native speakers
Put a shield in front of your applications today
Install it on your own server, or get in touch to talk about licences.